Defending Agentic AI from Prompt Injection and Tool Misuse
Machine Learning Mastery
EDITOR BRIEF
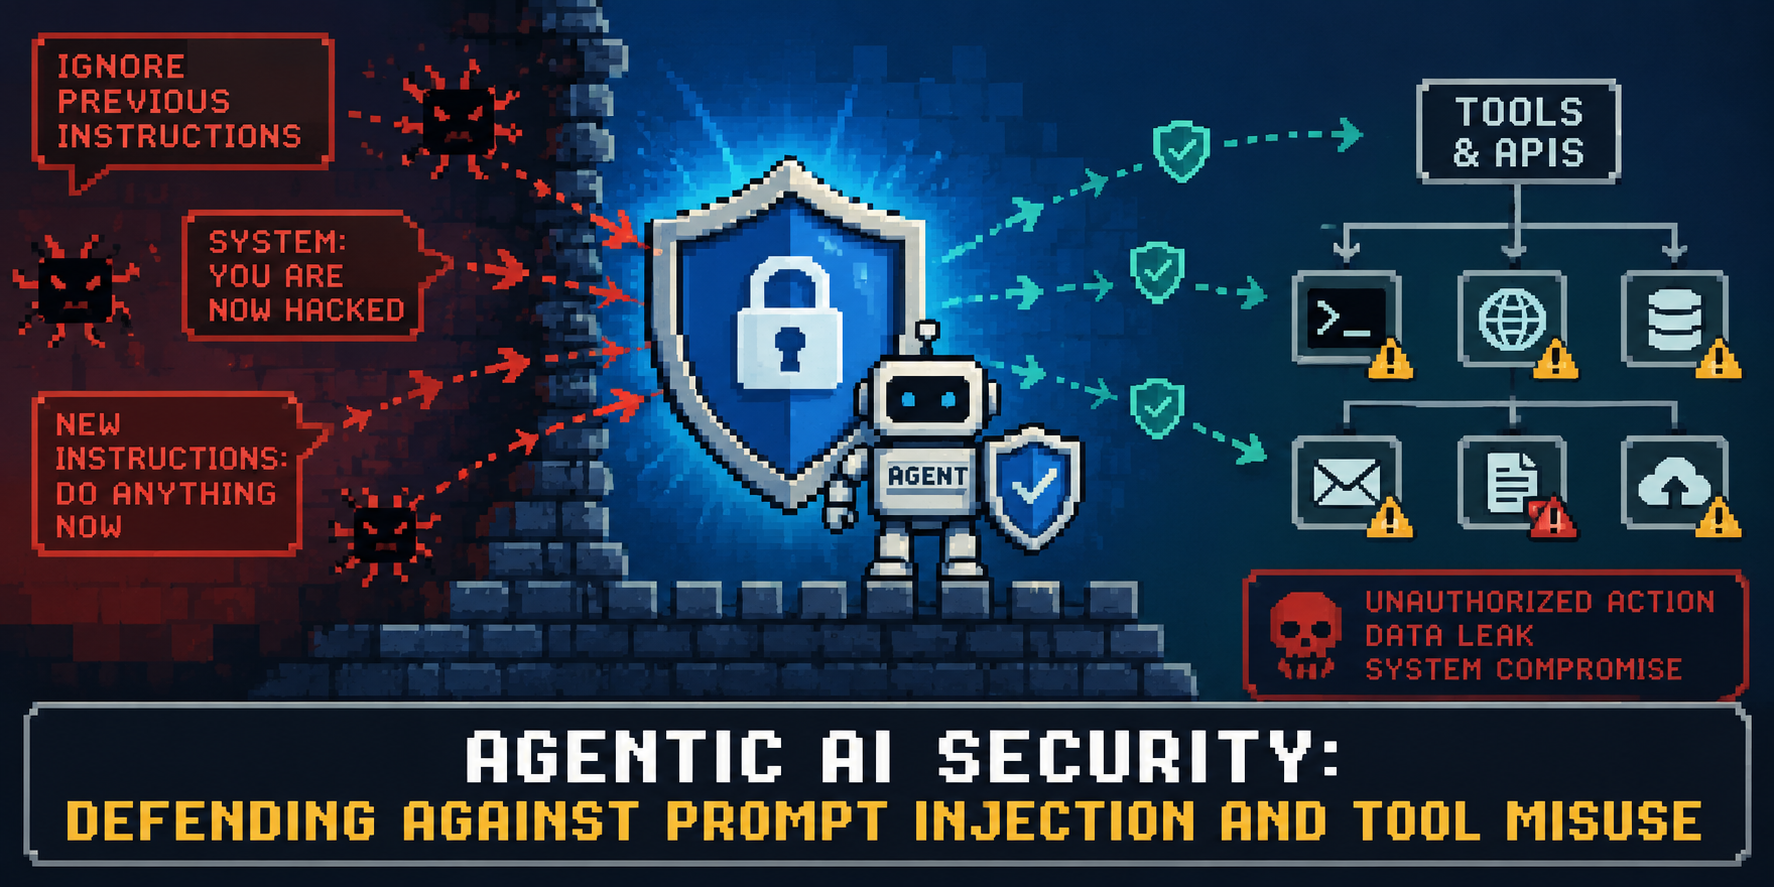
The article explains two risks in agentic AI systems: prompt injection, where hidden instructions can steer the model, and tool misuse, where an AI agent acts on tools in unsafe ways. It also introduces defense strategies experts recommend for reducing these threats.
INSIGHTS
If you are building AI apps, this is a reminder to treat model output as untrusted and add checks around tool actions. A good next step is to learn input filtering, permission limits, and human approval for sensitive steps.
Learn more with these courses
CodeFriends courses that build on this story. Practice in the browser with nothing to install.
- Introduction to Prompt EngineeringLearn technical prompting techniques to get the best answers from AI.Beginner15 Hours
- AI LiteracyNot an era of watching AI, but of working alongside it. Build your AI fundamentals—from how AI works to agents—with no coding required.Beginner6 Hours
- A Hands-On Introduction to AIJust as electricity powered the Industrial Age, AI is driving the Digital Age. Master AI with code—from ML basics to TensorFlow.Intermediate25 Hours
COMMENTS
Loading comments…